


CNIL lawyer
From risk anticipation to pre-litigation and litigation
Whether it's an innovative project involving personal data, a complaint, an audit, a data breach, a formal notice, or a sanction procedure, Odoné supports its clients when the stakes become sensitive or strategic. Leveraging our deep understanding of CNIL practices, we help organizations anticipate regulatory risks, define their positions, and develop tailored strategies for each situation, from initial project discussions to defense before the restricted committee.

Tailored support for each situation
Innovative or Sensitive Project
Some projects involving particularly sensitive or innovative processing of personal data (biometrics, geolocation, use of artificial intelligence, activity monitoring, data cross-referencing, etc.) require a prior analysis to anticipate regulatory risks and secure key structural choices before deployment.
Assisting a mobility operator in analysing the GDPR qualification (data controller, data processor or joint controllers) applicable to a complex data-sharing scheme involving mobility organising authorities.
Defining the data governance model and the allocation of responsibilities between the parties.
Complaint
Following a complaint, the CNIL may ask a company to provide explanations and supporting documents within a specified timeframe. The company's response is an important step in the handling of the complaint and may influence how the CNIL proceeds with the case.
Support for a CAC 40 group following a complaint filed with the CNIL concerning commercial prospecting activities carried out by one of its partners.
Defining the response strategy and providing assistance throughout discussions with the authority.
CNIL Inspection
The findings made by the CNIL and the information gathered during the inspection can significantly influence the outcome of the case. Thorough preparation for the inspection, followed by the analysis of the official report and the definition of an appropriate strategy, are often crucial.
Assisting a CAC 40 group facing a documentary inspection by the CNIL concerning an innovative biometric payment system, in a context of high media exposure.
Defining the response strategy and assisting throughout communications with the authority.
Data Breach
A data breach requires a rapid assessment of the risks associated with the incident to determine the applicable notification obligations. This analysis notably determines the notification to the CNIL and, where applicable, the information provided to the data subjects concerned.
Assisting a trade union following a data breach affecting several thousand sensitive data points related to its members.
Defining the notification strategy to the CNIL and assisting in preparing information for the data subjects concerned.
Formal Notice
The formal notice sets a deadline to remedy the shortcomings identified by the CNIL. The challenge is to assess the expected corrective measures and the risks associated with a lack of or insufficient compliance.
Assisting an American company following a formal notice from the CNIL concerning the use of cookies and other trackers.
Defining the response strategy and assisting in communications with the authority until the case was closed without further action from the CNIL.
Sanction Procedure and Appeals
When a sanction procedure is initiated, the challenge is to analyze the shortcomings identified by the CNIL and define an appropriate defense strategy to limit the consequences associated with the procedure. This strategy is notably implemented through written observations and preparation for the hearing before the restricted committee.
Assisting a mid-sized company during a sanction procedure initiated by the CNIL following a personal data breach.
Defining the defense strategy and providing assistance throughout the procedure, which led to halving the initially proposed sanction amount.
A close-knit team,
committed to excellence

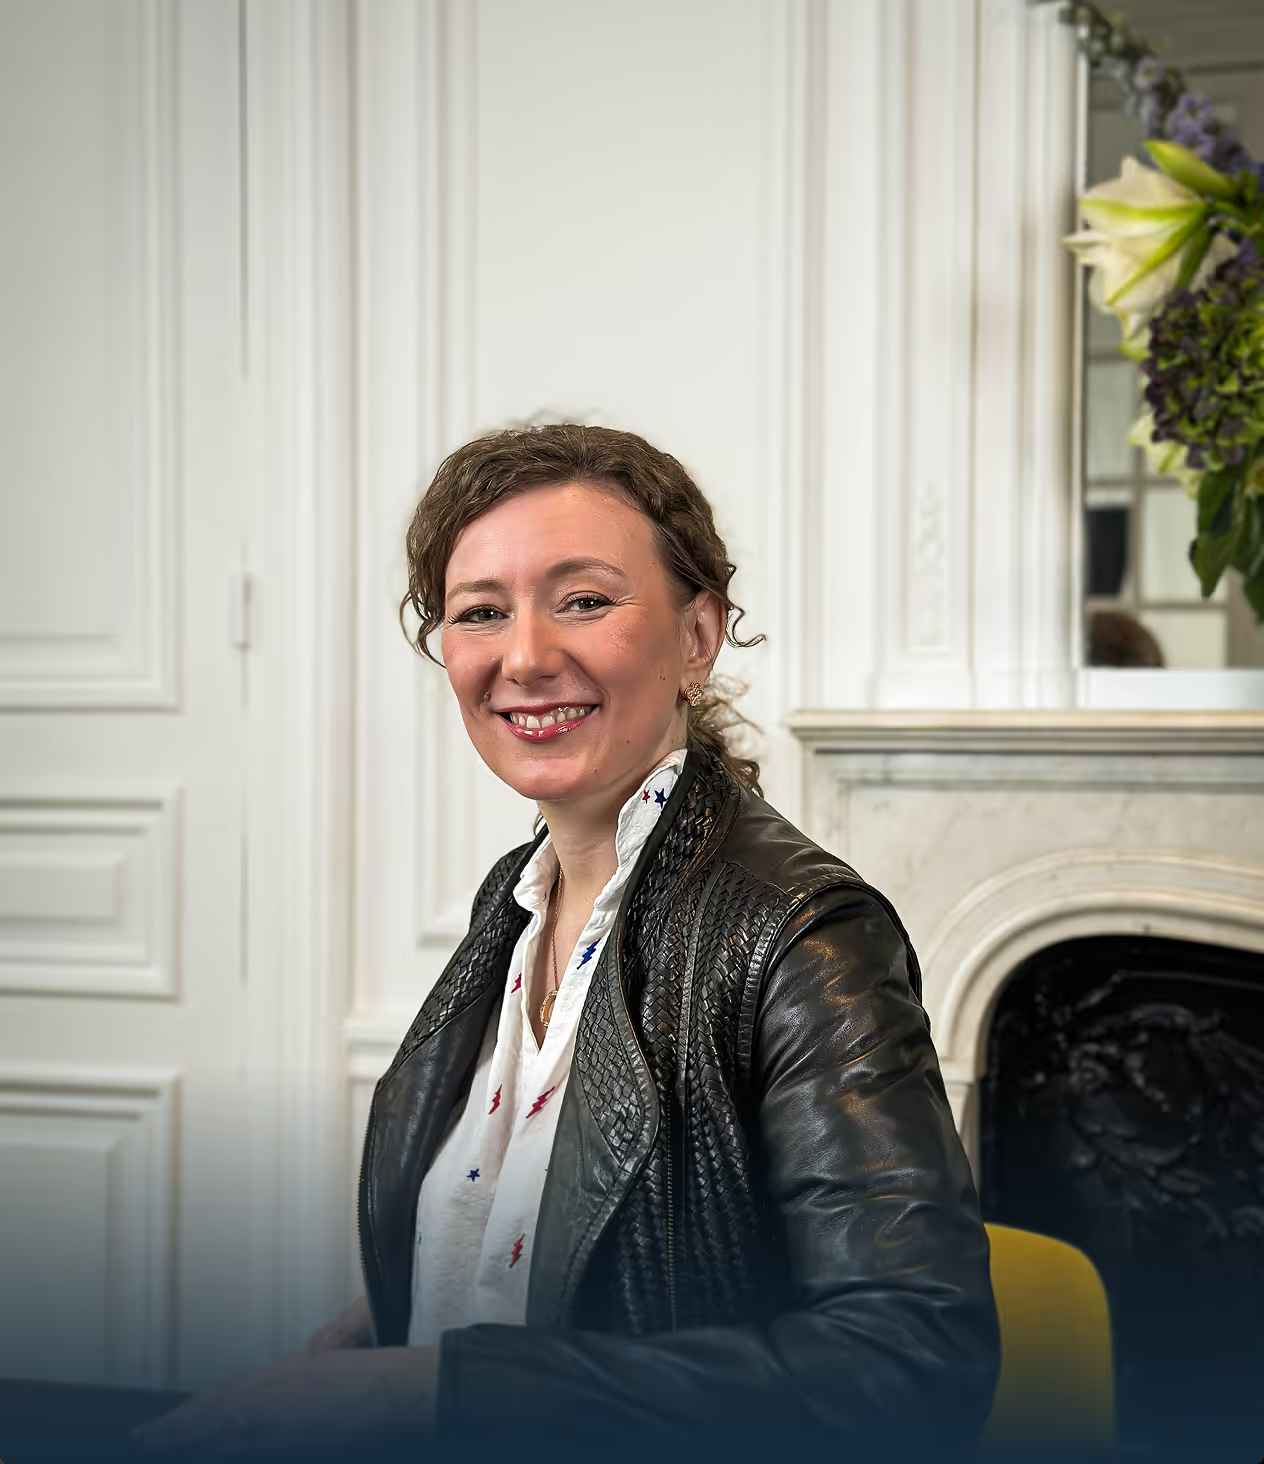
Joanna Masson
Before founding Odoné, Joanna spent seven years in leading international law firms.
She then joined the French Data Protection Authority (CNIL), where she worked within the Compliance Directorate and later in the Sanctions Department.
In this role, she supported major corporations, private-sector organisations and government ministries in their GDPR and French data-protection compliance efforts.
Since 2022, Joanna has also been a lecturer in data-protection law at École des Ponts ParisTech.
She holds a dual Master’s degree in French and English law (University of Cambridge and Paris II Panthéon-Assas), a Master’s degree in Industrial Property Law (Paris II), and a Master’s degree in Private Law (Paris I Panthéon-Sorbonne).
“Supporting a client means reconciling legal requirements and operational reality. Our mission: to provide clarity and security in a constantly evolving framework and to translate legal requirements into concrete solutions.”
— Joanna Masson


Emma Hanoun
Member of the Paris Bar since 2022, Emma works alongside Joanna.
Emma started her career in the legal department of a large international group, before joining a boutique firm where she managed the IT department as a counsel.
She holds a Master’s degree in Private Law (Paris II Panthéon-Assas), a University Diploma in Technology and Digital Law (Paris II Panthéon-Assas), and a Master’s degree in Multimedia and IT Law (Paris II Panthéon-Assas).
“Compliance is a corporate culture before it is a legal requirement. It is a marker of trust and a factor of credibility.”
— Emma Hanoun
Odoné, the expertise chosen by
the most demanding companies
Executives, in-house counsel, DPOs and former CNIL colleagues attest to the firm’s ongoing commitment to excellence, grounded in rigor, proximity and determination.
“I regularly work with Me Joanna Masson on matters involving personal data.
Her support has consistently been effective, marked by professionalism, responsiveness and an ability to adapt to each situation.
Her diverse experience and in-depth knowledge of the applicable regulations enable her to offer a pragmatic and rigorous approach.
Working with her is always a pleasure.”

“Joanna is a well-respected expert in data protection. Her strong subject-matter expertise and understanding of how companies operate enable her to balance legal constraints with business imperatives.”


“A highly competent, responsive and pragmatic lawyer who has supported us on a wide range of strategic projects. Joanna adapts smoothly to all types of stakeholders, and her risk-management approach was appreciated by everyone.”


“I work regularly with Joanna on complex and strategic data matters. She notably assisted us in conducting a mock CNIL inspection, from which we gained valuable insights. Joanna is responsive, dynamic and has an in-depth knowledge of the regulatory framework.”


“I worked with Joanna at the CNIL on several technically complex cases. She has a strong understanding of security requirements and quickly grasps technical issues. She is pragmatic, efficient and shows excellent judgement in her analyses. Working with her is a real pleasure. I recommend Joanna without hesitation!”


“Joanna is a highly skilled professional, with a deep data-protection expertise and working with her is always a pleasure. I was very pleased to have her as a colleague at the CNIL."

“Odoné assisted us both in contributing to a CNIL working group and in negotiating a public contract on complex data-protection matters. The firm combines solid expertise with pragmatic, responsive and close support for our teams.”


“I worked with Joanna for several years at the CNIL, notably on transport and energy matters. She has a deep and precise understanding of data-protection law and combines strategic vision with pragmatic judgement. She is able to assess complex issues rapidly and provide clear, practical advice.”


“Working with Odoné for several years on particularly sensitive data protection issues in the energy sector, we appreciate their responsiveness and pragmatism. Thanks to their detailed understanding of how the regulator works, they regularly assist us in complex situations, especially in the pre-litigation phase.”


“The Odoné firm supported us in our exchanges with the CNIL on complex personal data subjects, specific to the energy sector. Their regulatory expertise and the clarity of their analyses make them a trusted partner on the most sensitive issues.”

Let's discuss your challenges
Have you been audited by the CNIL, need to respond to a formal notice, experienced a data breach, or want to secure your practices?
Let's schedule an appointment now
Direct conversation with Joanna Masson, Founding Attorney
7 years of experience at CNIL
3 years with CNIL's enforcement team
Advisory for CAC 40 companies and mid-sized businesses
Clear guidance begins
with precise answers
How is your experience at the CNIL an asset?

Our years of experience at the CNIL, particularly within the sanctions department, enable us to anticipate the authority's expectations and quickly identify the key issues of a case.
Does a data breach always need to be reported to the CNIL?
No. Notification to the CNIL is only required when the breach is likely to pose a risk to the rights and freedoms of the individuals concerned. A case-by-case analysis must be conducted to assess the applicable obligations and the measures to be implemented.
Does a CNIL inspection necessarily lead to a sanction?
No. An inspection can lead to the closure of the case, a formal notice, or, in some cases, the initiation of an ordinary or simplified sanction procedure. Certain mistakes made during or after the inspection can, however, increase the risk of a sanction.
Does a complaint filed with the CNIL necessarily lead to an inspection?
No. A complaint does not automatically lead to an inspection or a sanction procedure.
Nevertheless, complaints are one of the CNIL's main sources for investigations. Depending on the nature of the reported facts and the responses provided by the organization concerned, the CNIL may request further explanations, initiate an inspection, or decide to close the case.
What is the role of a lawyer during a CNIL inspection?
A lawyer can intervene before, during, and after a CNIL inspection. Prior to the inspection, they can prepare the organization through a mock inspection, review existing GDPR documentation, and identify key areas of concern. They can also assist the organization on the day of the inspection to secure exchanges with the CNIL and support the teams involved.
A lawyer's involvement is often most valuable after the inspection. Analyzing the official report helps identify shortcomings noted by the inspection team, assess the associated risk level, and anticipate potential follow-up actions. The lawyer also assists the organization in its communications with the inspection services to inform them of corrective measures implemented and, where possible, demonstrate the organization's compliance. The goal is to avoid a passive approach to the case and to usefully contribute to the CNIL's decision on the follow-up to the inspection.
When should you seek legal assistance?
From the very first interactions with the CNIL. The explanations provided to the CNIL during a complaint, a data breach notification, or an audit can significantly influence the outcome of the case.